Tom C. Vincent II

Tom C. Vincent II

(He/Him)
recognized lawyers icon Recognized in Best Lawyers since 2024
Awarded Practice Areas
FinTech Practice Privacy and Data Security Law
Works at
Pierson Ferdinand LLP

56 Best Lawyers awards

Biography

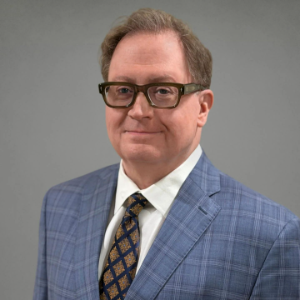
Tom Vincent is a Partner at Pierson Ferdinand LLP in Washington, District of Columbia. He is a Certified Information Systems Security Professional (CISSP), Certified Regulatory Compliance Manager (CRCM), and Certified Information Privacy Professional (CIPP/US). Tom advises financial institutions, technology companies, startups, and healthcare organizations on cybersecurity, data privacy, regulatory compliance, and corporate governance.

With more than 20 years of experience in banking and regulatory leadership, Tom has served as Chief Compliance Officer, BSA/AML Compliance Officer, HIPAA Compliance Officer, and Corporate Secretary. This experience informs his practical approach to helping clients address regulatory obligations, cybersecurity risks, privacy programs, data governance, and organizational accountability.

Tom’s practice includes the FinTech Practice and Privacy and Data Security Law. He counsels clients on privacy and security compliance, incident preparedness and response, financial technology regulations, corporate governance, and the legal and operational considerations associated with emerging technologies. His work considers not only technical and regulatory requirements, but also the relationship between data, identity, autonomy, trust, and corporate responsibility.

Tom also serves as an Adjunct Professor of Cybersecurity Law and Policy at The University of Tulsa College of Law. In that role, and through his work mentoring privacy practitioners, he explores the intersection of law, technology, ethics, and inclusion while supporting the professional development of lawyers, compliance officers, and privacy and security professionals.

Works at
Pierson Ferdinand LLP

56 Best Lawyers awards

Locations

Education

  • Southern Methodist University, B.S.
  • Washington and Lee University, J.D., graduated 1994

Bar Admissions

  • District of Columbia, The District of Columbia Bar
  • Oklahoma, Oklahoma Bar Association

Affiliations

  • International Association of Privacy Professionals - Member
  • American Bar Association - Member
  • Tulsa County Bar Association - Member

Client Testimonials

Awards & Focus

Recognized in The Best Lawyers in America® 2027 for work in:
  • FinTech Practice
  • Privacy and Data Security Law
Additional Areas of Practice:
  • Securities / Capital Markets Law
  • IT Outsourcing Law
  • Securities Regulation
  • Technology Law
  • Financial Services Regulation Law
  • Corporate Compliance Law
  • Banking and Finance Law
  • Administrative / Regulatory Law
Awards:
  • Oklahoma Bar Association, 2023, Ada Lois Sipuel Fisher Diversity Award

Additional Information

  • Selected Experience
  • Designed, developed, and implemented compliance programs, including website disclosures, policies, training, and risk assessment processes, to meet HIPAA, FERPA, GLBA, GDPR, FTC, and other state, federal, and international legal and regulatory requirements, including:

    • Privacy and Security Compliance

    • Contract Administrations and Third Party Risk Management

    • Anti-Money Laundering Compliance, including Suspicious Activity and OFAC Reporting

    • Sweepstakes, TCPA, and Electronic Transactions Compliance

  • Design and draft client agreements for accounting and technology consulting firms, including website documentation and internal onboarding procedures.

  • Negotiate execution and termination of FinTech agreements, including incorporation of existing customer disclosures and responding to requests from banking agencies regarding compliance issues.

  • Engaged security firms for various clients to perform penetration testing and other security assessments, including management of request-for-proposal process and engagement agreement drafting and negotiation.

  • Served as insurance-approved breach counsel for privacy and security incidents to determine reporting responsibilities across multiple states, territories, and countries, including the development of required customer communications and direct communications with state and federal agencies.

  • Reviewed client insurance policies for appropriateness of coverage and provided responses to insurance carriers regarding the sufficiency of client breach responses.

  • Serve as compliance counsel for multimedia company providing online memberships and sweepstakes giveaways.

  • Selected Presentations and Podcasts
  • “Aligned by Design: CISO x Legal In Practice” (Secure AF Podcast - Alias Forensics), July 22, 2025

  • “The Ethics of Inclusion: Developing the Words, Actions, and Achievements to Change Yourself and Your Practice” (Lawline), June 8, 2023

  • “Proactively Managing Vendor Relationships: Setting Expectations, Avoiding Surprises, and Getting Your Stuff Back” (Lawline), February 22, 2023

  • “What Now? Post-Breach Cybersecurity Issues: Addressing the Obvious and the Hidden, Not-Initially-Visible, and Otherwise Neglected Causes and Consequences of a Data Breach” (SouthWest Benefits Association), November 8, 2022

  • “Beyond Attorney-Client Privilege: Reconciling Traditional Attorney Issues and an In-House Environment” (Association of Corporate Counsel), September 16, 2022

  • “IT/IT Security, and Legal; Building Mutually Beneficial Relationships” (ISSA), November 8, 2021

  • “Cool to be Kind: The Expectation of Positivity and the Need to Belong” (DisruptHR Tulsa), October 20, 2021

  • “Cybersecurity! Why All the Cool Kids Are Doing It” (with Trent Shores, Oklahoma Association of Municipal Attorneys), September 9, 2021

  • “Avoiding Unintentional Exclusivity: Why the Language We Use Matters” (National Conference of Bar Foundations), July 31, 2021

  • “We’ve Been Hacked! What Do We Do Now?” (ISSA CyberSecurity Roundtable), January 26, 2021

  • “Embrace Your Blur: Using Your Authentic Self to Create Your Career Brand Narrative” (Black Wall Street Chamber of Commerce), November 12, 2020

  • “Courageous Conversations: Beyond the Hashtags” (Mosaic & Luxa Enterprises), August 25, 2020

  • “Life Preservers and Safety Nets: Returning to Work and Staying Afloat in COVID-19’s Wake” (Tulsa Area Human Resources Association’s Learning Lab), May 28, 2020

  • “Oh, What a Tangled Web(site) We Weave” (GableGotwals and Stinnett & Associates Cyber Webinar), May 13, 2020

  • “It’s not what you do, it’s why you do it: Ownership, Obligation, and Information Security” (Workforce Forensics Podcast), April 30, 2020

  • “Unexpected Legal Ethics Work-at-Home Webinar” (Avansic Work at Home Webinars), April 15, 2020

  • “Courageous Conversations Year End Celebration: 50 Shades of Courage” (LUXA 2nd Annual Year End Celebration), December 18, 2019

  • “Best Practices of Employee On-Boarding/Off-Boarding” (Tulsa Area Human Resources Association Employment Law & Practices Seminar), November 7, 2019

  • “To Secure and Protect: Fulfilling the Expectations of Clients (and Others) in Commercial Real Estate and Fiduciary Transactions” (Tulsa Title and Probate Lawyers Association), June 13, 2019

  • Selected Writings
  • Client Alert: No Company Too Small: Safeguarding Privacy and Cybersecurity in Renewable Energy, August 12, 2025

  • “A Need for New Armor: Tribal Entities Under Cyberattack” (with Emma Kincade and Trent Shores), GableGotwals Cybersecurity and Data Privacy Alert, October 21, 2021

  • “Chapter 14: Energy Cybersecurity Law – A Survey” (with Susan Lindberg and Trent Shores), Energy Law and Transactions (Matthew Bender), October 2021

  • “This Is Your Lucky Day” (Gavel to Gavel, The Journal Record), January 29, 2020

  • “Breaches and Attorney-Client Privilege” (Gavel to Gavel, The Journal Record), September 18, 2019

Your browser is not fully compatible with our automatic printer friendly formatting.

Please use the print button to print this profile page.

Spinning circle Big letter B